
How Hackers Use APIs to Steal Money from Banks

Think about walking into a bank and asking for money, without any paperwork, no identity, no permission. That sounds impossible. But cybersecurity experts worry that a digital version of this scenario is becoming a reality for some financial institutions.
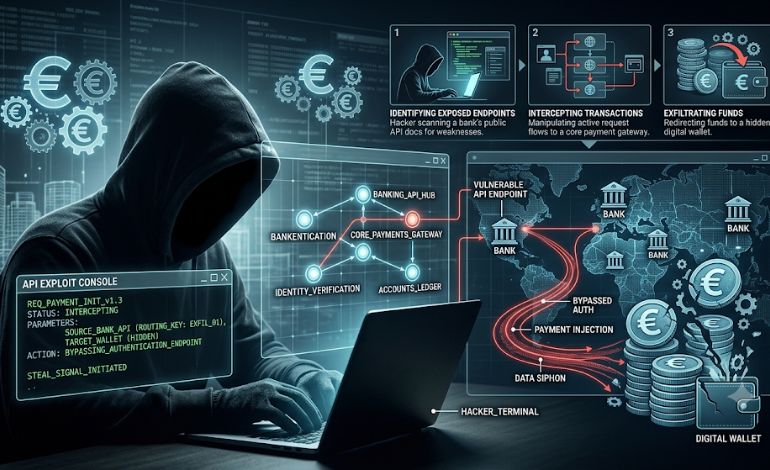
The CERT-In, India’s national cyber security organization, and the CSIRT-Fin, the financial sector response team, have released a critical advisory cautioning against a rising cyber threat to payment and distribution systems inside the financial industry. The alert states attackers are collecting API credentials and exploiting them to initiate unauthorised fund transfers using the financial institutions’ own systems.
APIs or Application Programming Interfaces are unknown technical terminology for most people. You might think of them as digital messengers that allow different systems and apps to talk to each other. Every time you use a banking app, make an online payment or transfer money digitally, APIs are typically at work behind the scenes to make it happen.
The concern is that cybercriminals are increasingly targeting these digital links.
Attackers are exploiting unprotected apps and APIs, stealing payment-related credentials, and directly accessing fund transfer operations, the alert said. As a result, attackers can bypass safeguards that ordinarily protect financial transactions, such as loan approval processes, beneficiary verification, KYC standards, and transaction controls.
Also Read:
Mark Heuring: Bridging the Gap Between Innovation and Real-World Healthcare Adoption
Trump Signs a Russian Diesel Agreement with Zelensky, calling it a gift for Putin